

Authenticator 2FA OTP Backup analysis by Appwee
When a household starts using two-factor authentication seriously, the difficult part is rarely the six-digit code itself. The real challenge is deciding whose account belongs on which device, who can reach the backup method, and what happens when a shared phone is replaced or unavailable. Authenticator 2FA OTP Backup is designed for this practical corner of digital life. I tested it as a security tool rather than treating it like another app to open every day, and I found that its value depends heavily on how carefully each account boundary is managed.
This is a free House & Home app from Duong Van Luong, with a 4.2 average from around 58 thousand ratings and over 1 million installs. Its short store description is simply “Authenticator 2FA,” while its broader purpose is to secure accounts with OTP codes, TOTP, and private two-factor login. That combination makes it relevant to families, roommates, and anyone managing several household services, but it does not remove the need for a sensible access plan.
Using it around a shared household device
A realistic example is a couple managing a home internet account, a utility portal, a streaming service, a shopping account, and a shared cloud subscription. One person may normally handle the bills, while the other needs occasional access when the primary phone is charging, lost, or being repaired. Installing one authenticator on a shared tablet or household phone can seem convenient because the codes are available in one place.
That convenience is also the first important warning. A one-time password is not a harmless reminder; it is part of the key used to enter an account. If everyone in the home can unlock the device and open the app, everyone with that access may be able to complete a login. I would therefore use this arrangement only for genuinely shared services, never as a casual container for one person’s banking, work, health, or private social accounts.
The app is most useful when the household first agrees on ownership. A shared grocery account and a private email account should not be treated alike. I would create a simple list outside the app showing the account owner, the recovery contact, and which device is allowed to generate codes. That small bit of preparation prevents a common mistake: putting every QR setup code into the same place just because the app makes it possible.
For a family with children, the distinction matters even more. A child may need access to a shared game or entertainment account, but that does not mean the child should see codes for an adult’s private services. Authenticator 2FA OTP Backup can be part of a household security plan, but it should not be mistaken for a family-management system. The app provides authentication functions; the household still has to decide who is trusted with each account.
What the first setup feels like
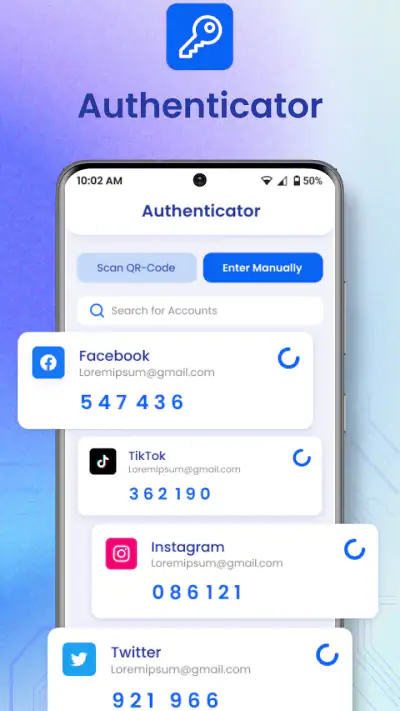
The initial workflow is familiar if you have used an authenticator before: add an account, scan or enter its setup information, and use the generated code during login. The important moment is not the scan itself. It is checking that the account label is clear enough to identify later. “Email” is a poor label in a busy household; a name such as “Alex personal email” or “Shared electricity account” reduces the chance of selecting the wrong code under pressure.
I also recommend testing each new entry immediately. Sign out of the service, sign in again, and confirm that the code generated by the app works before relying on it. This catches a mistyped secret or a time mismatch while the original account session is still available. Waiting until a phone has been wiped turns a small setup error into a stressful recovery problem.
The app supports OTP codes and TOTP, so it fits services that use standard time-based verification rather than text messages. That is a meaningful advantage over SMS in situations where a phone number is unavailable or messages arrive late. Still, it does not mean every account can use it. The service being protected must offer a compatible authenticator method, and the account holder must complete that service’s own security setup first.
One practical limitation is that an authenticator is only as dependable as its device and its recovery planning. If the household keeps all codes on one phone and that phone disappears, the app cannot magically recreate access. I would keep the account provider’s recovery codes in a separate, protected place and decide in advance who may retrieve them. Storing a second copy beside the phone defeats much of the point.
Keeping personal and shared accounts apart
My strongest recommendation is to treat the app like a key cabinet, not a general household drawer. Shared entries should be visibly separated from personal ones through consistent naming. If the app offers an organization method you prefer, use it; if not, careful labels still help. The goal is to avoid exposing a private code while someone is trying to log in to a shared service.
Before adding an account, ask three questions: who owns it, who needs access, and what happens if the device is handed to someone else? If the answer to the last question is uncomfortable, the account does not belong on a shared device. This is especially important for teenagers who borrow a parent’s phone, roommates who share a tablet, or relatives who use a household device during travel.
I would also avoid putting a work account into a family device unless the employer explicitly allows that arrangement. Workplace sign-ins may have stricter rules, and a shared household setup can blur responsibility. The same caution applies to accounts containing financial information, private correspondence, or documents belonging to only one person. A separate personal device, protected by its own lock, is the better choice there.
Coordinating access without making security weaker
Household coordination is where this app can either become genuinely helpful or create confusion. If two adults share responsibility for a service, they should agree on a handover process before one person travels. That might mean confirming that both know the account recovery route, rather than simply copying every code to both phones. The latter feels convenient, but it increases the number of places that must be protected.
A useful routine is to review shared entries whenever an account changes hands. Remove access from an old household device, update labels after a roommate moves out, and check whether a service has changed its two-factor settings. These actions are not glamorous, but they matter more than opening the authenticator repeatedly. The app generates codes; it does not decide when an old device should no longer be trusted.
For a shared account, I prefer two independent authorized devices when the service supports that arrangement, with each device belonging to a responsible adult. That is safer than a single communal phone because one person’s lost device does not automatically lock out everyone. However, adding more devices also creates more exposure. I would keep the number small and record exactly who has access.
There is a trade-off between convenience and separation. A household tablet in a common room is easy to reach, but it offers weaker privacy than a locked personal phone. A personal phone is better for account boundaries, but it may be unavailable when the household needs the code. Authenticator 2FA OTP Backup does not solve that trade-off; it makes the choice visible, which is useful in itself.
Age, trust, and the meaning of “Everyone”
The app carries an Everyone content rating, so its subject matter is suitable for general audiences. That should not be confused with unrestricted access to every stored code. A young user can understand how to read a verification code while still not being the right person to manage an adult’s account keys. Age is only one part of the decision; maturity, account ownership, and the consequences of misuse matter just as much.
For older relatives, the app may be helpful if they find text-message verification unreliable or difficult to manage. I would set it up alongside them, use clear labels, and practice one normal login without rushing. The biggest risk is not usually the code display; it is confusion about which service is requesting it. A calm, descriptive naming system can make the process much easier.
For children, I would keep the setup limited to accounts they are genuinely allowed to use. I would not hand over a device containing a parent’s complete authentication collection merely because the child needs one code. If a child is responsible enough to manage a shared account, explain that codes are private and should never be sent in a chat, read aloud to strangers, or entered into an unexpected page.
Trust also changes over time. A former roommate, an ex-partner, or a family member who no longer uses a shared service should not retain access simply because the app still works on their phone. The account owner needs to remove that device or regenerate the two-factor setup through the service. Keeping an old copy active is an easy oversight, especially when access was originally granted informally.
How it compares with the usual alternatives
The most obvious alternative is SMS verification. A TOTP authenticator can be more dependable when messages are delayed, a phone number changes, or mobile coverage is poor. It also keeps the code-generation step within the authentication app instead of depending on a carrier message. On the other hand, SMS may be simpler for relatives who rarely use apps, and some services still make it the easiest recovery route.
Another alternative is a password manager with built-in one-time-password support. That approach can be better for someone who wants passwords, passkeys, notes, and codes in one carefully protected vault. It may also make account migration more organized. A dedicated authenticator such as this one is more focused and can feel less cluttered, but it means maintaining another security tool and planning separately for password recovery.
Hardware security keys are stronger for people facing serious account-targeting risks or managing important work systems. They reduce dependence on a phone’s screen and code entry, but they cost more and require compatible services. For an ordinary household that needs TOTP for a few shared subscriptions or utility accounts, Authenticator 2FA OTP Backup is likely easier to introduce. For high-value accounts, I would consider a hardware key or the provider’s strongest available method instead of relying on one app alone.
Compared with keeping codes in screenshots or notes, the app is plainly the safer and more suitable choice. Screenshots can appear in photo backups, sync to other devices, or be viewed accidentally. A plain note is easy to copy and hard to audit. An authenticator keeps the workflow centered on temporary codes, although the security still depends on the phone lock, the app’s own protection, and the care taken during setup.
Small habits that make the app safer to live with
First, do not confuse a successful login with a complete backup. After adding an account, locate that service’s recovery codes and decide where they will live. The authenticator may help you sign in today, but recovery codes are what can save you after a lost phone, a broken screen, or an accidental reset.
Second, check the device clock if codes repeatedly fail even though the setup secret was entered correctly. Time-based codes depend on accurate time, so an incorrect automatic time setting can look like an app problem. I would correct the device time before deleting and re-adding an account, because re-enrollment can create unnecessary work and may invalidate the original setup.
Third, use a naming convention that survives household changes. Include the service and the person or group responsible for it, rather than relying on a vague nickname. This is especially valuable when a visiting relative or a second adult needs to select the right entry quickly. Clear labels are a simple form of error prevention that many first-time users overlook.
Fourth, review the collection after a move, breakup, device upgrade, or change in responsibility. Delete entries that no longer belong on that device only after confirming that the account has another working authentication route. Removing blindly can lock out the rightful owner; leaving everything untouched can expose someone who should no longer have access.
Finally, treat the app’s free availability as an opportunity to test the workflow before committing household accounts to it. The app is free to install, while in-app purchases range from around six dollars to around thirty dollars per item. I would not make a purchase decision based only on the presence of optional paid items; first determine whether the everyday code process, labels, and recovery habits fit the household.
Who should use it and who should choose something else
I think this app suits people who want a focused way to generate authenticator codes without placing those codes in text messages or ordinary notes. It is a sensible fit for a technically comfortable adult managing a handful of compatible accounts, and it can work for shared household services when ownership and device access are clearly defined.
I would be more cautious recommending it to someone who expects effortless account transfer between family members, automatic recovery after losing a phone, or a complete family permission system. Those expectations go beyond the basic job of an authenticator. A password manager may be a better match for someone who wants one protected place for credentials and codes, while a hardware key may be preferable for high-risk accounts.
The app is also not ideal as a communal dumping ground. The more private accounts it contains, the harder it becomes to lend the device safely. If several adults need independent privacy, separate protected devices and individually managed account access are better than one shared collection. Convenience should not become an excuse to erase boundaries.
Version 2.5.22 supports devices running Android 7.0 or later, which makes it approachable for people keeping an older Android phone in service as a backup device. That can be useful in a household, but an older phone should still have a screen lock and receive whatever system security updates are available. A compatible operating system alone does not make a neglected device a safe place for authentication codes.
My household verdict
After using Authenticator 2FA OTP Backup with the household angle in mind, I see it as a practical, focused tool rather than a complete security strategy. Its strongest quality is straightforward: it gives compatible accounts a dedicated place for OTP and TOTP codes, avoiding the delays and exposure that can come with SMS or screenshots. The fact that it is free and rated for Everyone lowers the barrier to trying it, while its popularity suggests that many people are already comfortable with the basic idea.
My recommendation comes with a firm condition: keep account boundaries visible. Put shared services on a shared device only when every person with access is meant to have that access. Keep private, financial, work, and sensitive accounts on a personal device. Maintain recovery codes separately, test each new setup, and review access after household changes.
For my own everyday use, I would choose this app for a small collection of compatible household accounts and label every entry carefully. I would not use it as the only protection for my most important accounts, nor would I assume that a shared phone is automatically a safe backup. Used with those limits, it can make two-factor login less dependent on text messages and less chaotic for a busy home. Used without those limits, it can turn one convenient device into a single point of privacy failure.
Gallery
Authenticator 2FA OTP Backup Pros and Cons
- Supports secure two-factor authentication with time-based OTP codes.
- Backup options help prevent losing access when changing or resetting devices.
- Simple interface makes adding and managing multiple accounts straightforward.
- Works without a constant internet connection once accounts are configured.
- Useful for protecting email
- social media
- banking
- and other online accounts.
- Some backup features may require extra setup or a paid upgrade.
- Losing the backup password can make restoring stored accounts difficult.
- The app may feel limited compared with established authenticator alternatives.
- Moving accounts between devices can require manual verification steps.
- Incorrect device time settings may cause generated codes to fail.
Authenticator 2FA OTP Backup Frequently Asked Questions
What is Authenticator 2FA OTP Backup, and what does it do?
Authenticator 2FA OTP Backup is designed to generate time-based one-time passwords (TOTP) for accounts that support two-factor authentication. After setup, it provides a rotating verification code in addition to your password when you sign in. The backup feature is intended to help preserve or restore your authenticator entries, although you should still verify exactly how backup and recovery work before relying on them.
Can I use Authenticator 2FA OTP Backup with popular online accounts?
In most cases, the app can work with services that support standard authenticator-app verification, including many email, social media, cloud storage, financial, and gaming platforms. During setup, you normally scan a QR code or enter a secret key manually. Compatibility depends on the service using a supported OTP standard, so check the account’s security settings and test the generated code before signing out.
How does the backup and recovery feature work?
Backup and recovery are especially important because losing access to an authenticator can lock you out of protected accounts. Authenticator 2FA OTP Backup may provide a way to save or restore your OTP entries, but the exact process can depend on the app version, device, and storage method. Keep recovery codes from each online service in a separate secure location as an additional safeguard.
Is Authenticator 2FA OTP Backup safe to use?
An authenticator app can improve account security because it generates codes locally instead of sending them by text message. However, your protection also depends on how the app stores secrets, handles backups, and protects access to the device. Use a strong device passcode, install the app only from an official store, review requested permissions, and avoid sharing screenshots or backup files containing your OTP information.
What should I do if I lose my phone or the generated code is rejected?
If your phone is lost, use the account’s recovery codes, a previously registered security key, or another approved recovery method to regain access. If a code is rejected, check that your device’s date and time are set automatically, since time-based codes expire quickly. Do not immediately delete the account entry; first confirm the setup key, service compatibility, and recovery options.














